netbank
A prototype of a bank you don’t have to take at its word. Accounts live in a shared chain of blocks kept by independent nodes, and clients check their own balances.
The idea
In an ordinary bank the client trusts the statement. Here we wanted an operator’s mistake or fraud to be provable, not just noticeable.
How it works
Money moves only with the client’s Ed25519 signature. Roubles are issued by a single gateway. Witnesses re-execute every block and sign it, and a block is final once a quorum signs: two of three. An operator who signs two different blocks at the same height ends up in the fraud evidence.
The client cabinet
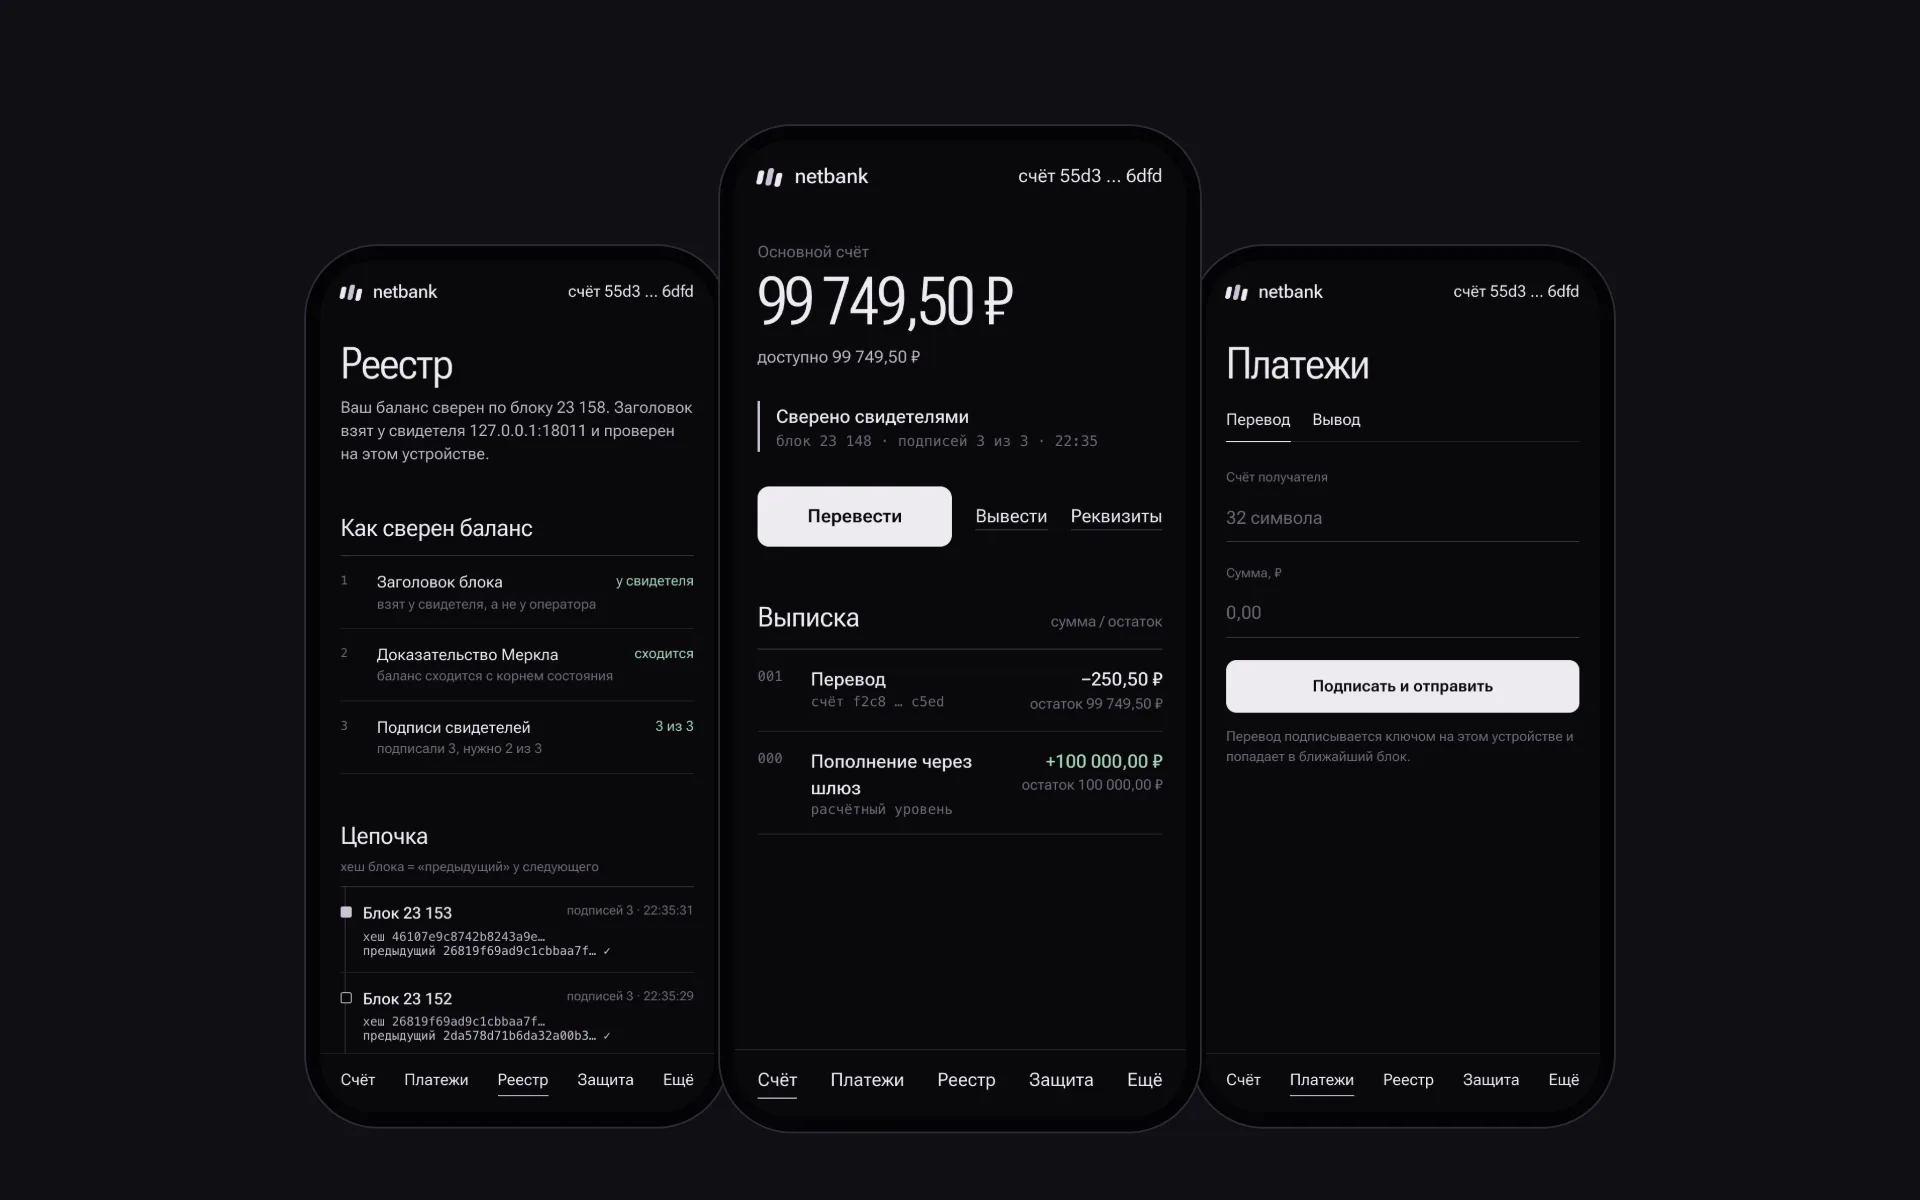
The cabinet installs on a phone like an app. The key stays in the browser, and the balance is checked with a Merkle proof against the block header from a witness, not from the operator. An account can be frozen only openly, with a reason and a term. The cabinet also has a delay for large transfers, guardians of whom any two of three can restore the key, and a delayed key change.
Honest limits
It is a prototype. Operator rotation falls short of full BFT, keys in the browser are for demonstration, and there is no TLS between nodes.
A block sealed by a quorum
The ledger is a book and a block is a page. The operator’s lever only turns pages; a page is sealed when at least two of the three witness seals come down.
Screens
Under the hood
- C++20: a deterministic core with no network, disk or clock, a block chain and a node with an HTTP API.
- Monocypher: Ed25519 signatures and BLAKE2b hashes, a Merkle proof for every account.
- A demo network in Docker Compose: two operators, three witnesses and a regulator.
- Web clients check signatures and proofs right in the browser: the explorer, the cabinet and the operator panel.
- A Python cross-check of the arithmetic and an “evil operator” scenario that the witnesses catch.
C++20 · Monocypher · Ed25519 · Merkle · Docker · PWA